 Transaction risk intelligence
 Automated supplier statement reconciliation
 Supplier risk intelligence
 Managed AP recovery audit
 Supplier file performance review
 Forensic risk analysis
 Consulting and bespoke reporting





Please note that FISCAL Technologies have written this blog to share best practices based on Government guidelines. We implore you to seek legal counsel and to consult the Government website for more information about this law.
*Updated March 2026*
We’ve seen the headlines.
The Economic Crime and Corporate Transparency Bill 2023; the ‘Failure to Prevent Fraud’ is a criminal offence. It came into effect on the 1st September 2025.
In the future, we’re expecting to see further crackdowns on identity verification and filing.
What does Failure to Prevent Fraud mean for companies like yours?
According to the UK Government website, ‘an organisation [is] liable where a specified fraud offence an employee or agent commits the offence, for the organisation’s benefit, and the organisation did not have reasonable fraud prevention procedures in place’.
Please note that this also applies to subsidiaries or other ‘associated persons’ who provide services for, or on behalf of the organisation, for example, outsourced payroll personnel and contractors. Your organisation don’t need to be aware of, or order, the fraudulent activity to be liable. It just needs to happen and benefit the organisation.
ECCTA legislation is designed to strengthen the existing powers to fine and prosecute organisations, closing loopholes. Those unlimited fines can be a hefty penalty. Companies House now have powers to validate and strike off companies, while the Serious Fraud Office, Companies House and the National Crime Agency are all able to share information.
Furthermore, although this is a UK law, it applies to organisations outside of the UK if the perpetrator commits the offence in the UK or targets UK victims.
This creates an onus on companies to ensure they have effective fraud-prevention measures in place, and to prove it if asked.
The punishment for this offence is unlimited fines, and we can expect the fines to be proportionate to the scale of the fraud, the organisation’s financial condition, their level of controls, and their co-operation with authorities.
Who does the failure to prevent fraud offence apply to?
The ‘Failure to Prevent Fraud’ offence applies to large companies. These are organisations meeting at least two of the following: ‘More than 250 employees, more than £36 million turnover and more than £18 million in total assets.’
If this is the case for you, it’s prudent to review your current fraud prevention policies and procedures immediately. Since companies from outside the UK can also be prosecuted, we recommend any company where this applies should take precautions.
So specifically, the offence applies to:
- All large, incorporated bodies, subsidiaries and partnerships.
- Large not-for-profit organisations such as charities, if they are incorporated.
- Incorporated public bodies.
- Bodies, incorporates and partnerships formed outside UK, with a UK nexus.
Other companies can also benefit from taking further preventative measures, even if the laws currently do not apply. It’s possible that because of this law, medium-sized companies may become the target of fraud as large companies’ checks become more stringent. From that viewpoint, it’s a good idea for any company to prepare for this change by having thorough fraud prevention measures in place.
What falls under the Failure to Prevent Fraud law?
For the law to apply, the fraudulent activity should benefit the business and be undertaken by an associated person. This could be an employee, agents, subsidiary or intermediary. Anyone who performs services for, on behalf of the organisation. This does not include a supplier to the organisation.
Please note that if the fraudulent activity was intended to be only for the individual’s benefit and the company was a victim of the fraud, this law does not apply.
Offences that fall under this law include:
- Fraud by false representation.
- Fraud by failing to disclose/omitting information.
- Fraud by abuse of position.
- Participation in a fraudulent business.
- Obtaining services dishonestly.
- Cheating the public revenue.
- False accounting.
- False statements by company directors.
- Fraudulent trading.
Guidance on ‘Failure to Prevent Fraud’ offence
The Government has now published guidance on this offence, with Nick Ephgrave QPM, Director of Serious Fraud Office (SFO) saying: “The publication of this guidance means that time is running short for corporations to get their house in order or face criminal investigations.”
How can we defend against the ‘failure to prevent fraud’ offence?
To comply with the law, organisations must show that: ‘They have reasonable procedures in place to prevent fraud, or if they can demonstrate to the satisfaction of the court that it was not reasonable in all the circumstances to expect the organisation to have any prevention procedures in place.’
What does a reasonable fraud prevention procedure look like?
According to the guidelines set out by the Government, a reasonable fraud prevention framework should be informed by the following principles:
- Top-level commitment
- Risk assessment.
- Proportionate prevention procedures.
- Due diligence.
- Communication and training.
- Monitoring and review.
To prevent fraud, companies should consider how they can reduce fraud opportunity, motive and rationalisation of fraud, create consequences for committing fraud, and thoroughly test their fraud prevention measures.
In terms of practical compliance, there needs to be a Governance process and robust controls over finances, operations, technology and contracts.
Overall, companies should complete fraud checks which are appropriate to their risk level.
For example, a 5000 person organisation with 10 divisions should have far more stringent measures in place than a 500 person organisation with 3 divisions.
We recommend:
- Completing fraud risk assessments regularly while considering the fraud triangle, and documenting them well. You may also need to complete a gap analysis to ensure your procedures are watertight.
- Develop clear, practical procedures relevant to your risk level and organisational complexity.
- Fostering an anti-fraud culture within your organisation by providing awareness and educational programmes for employees and other associates. best practice with this includes role-specific training and specialised training for high-risk positions, with practical scenario-based exercises and regular refresher training.
- Setting up a whistleblowing system or procedure is essential, as is communicating how to use it and reminding staff regularly.
- Conducting thorough due diligence on all staff, contractors, suppliers, volunteers and other associated persons when onboarding. This could include background checking and police checking employees.
- Monitoring, updating and reviewing your policies and procedures often, incorporating feedback, audits and best practice.
- Communicating fraud prevention policies and procedures clearly and regularly.
- Increasing risk prevention measures during particularly risky times.
- Completing audits and monitoring financial data regularly.
- Maintain high documentation standards, including thorough records of risk assessments, mitigation actions, authorisation procedure, monitoring and testing activities and any management decisions made regarding fraud prevention.
Further controls for strong fraud prevention and detection include using third party risk management tools:
- Tracking changes in supplier payment information.
- Reviewing your master supplier file often and cleansing it of duplicate suppliers, one-time suppliers, dormant suppliers and incorrect suppliers.
- Monitoring inconsistencies in accounts receivable and payable to identify fraud indicators.
- Comparing staff information against master supplier files, and alerts when there is an alteration to the master supplier file.
- Checking purchase card expenses and other expense claims regularly.
- Backing up your records and having a transparent and complete audit trail.
- Making employees and associates aware of your anti-fraud measures as a deterrent and being transparent with staff about the penalties.
We also recommend that your risk detection software is up to date and that your team log in often to check risks. Having evidence of your fraud prevention procedures is a vital step in being able to prove you have a reasonable procedure in place.
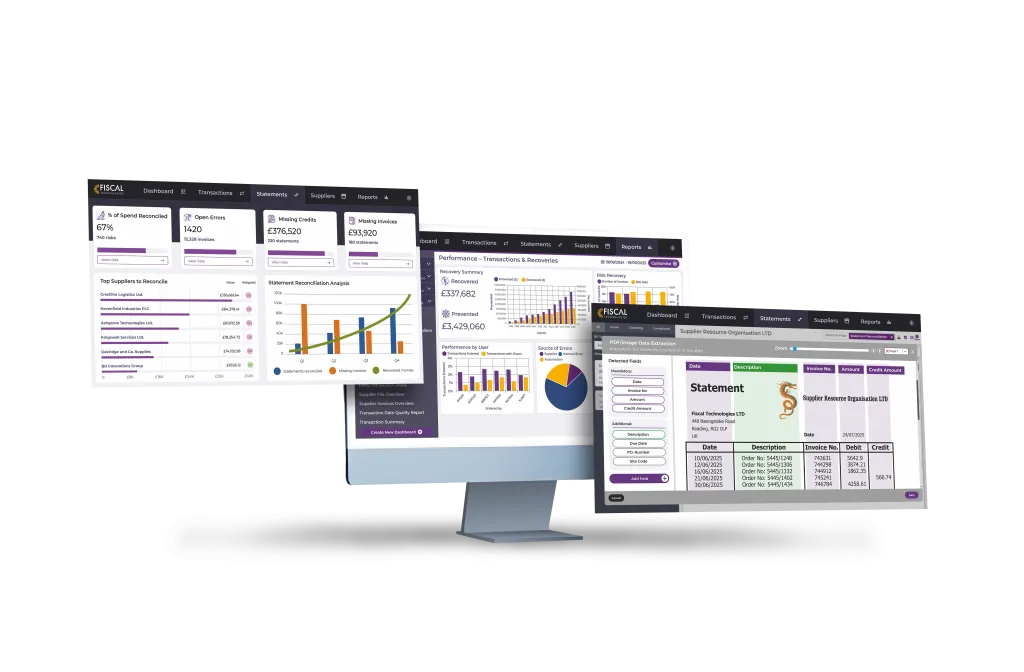
How FISCAL helps your organisation check for internal fraud.
Our P2P risk management software makes it easy to identify fraud risks and take action faster. Using advanced forensics and AI, our platform completes continuous analysis of suppliers and transactions to identify fraud risks. Those checks include:
- Employee-to-supplier credential matching.
- Checking the master supplier file for issues including dormant accounts, changes to the file, and duplicate suppliers.
- Identifying unusual supplier payments, such as round amounts, and exceptions or inconsistencies in transactions.
- An audit trail to discover who has made changes, and when.
Using our fraud prevention software allows you to have greater control around your spend, and who you spend with. It gives a high level of oversight, giving you peace of mind.
For more information on the failure to prevent fraud offence, please visit the UK Government website here.

6 supplier statement reconciliation issues you can improve now

One simple way to improve supplier relationships through accounts payable
Supplier Statement Reconciliation: What it is & why it matters for AP
Your cheat sheet to boosting invoice processing efficiency